Microsoft Project Solara: The Operating System for Workplace AI Agents
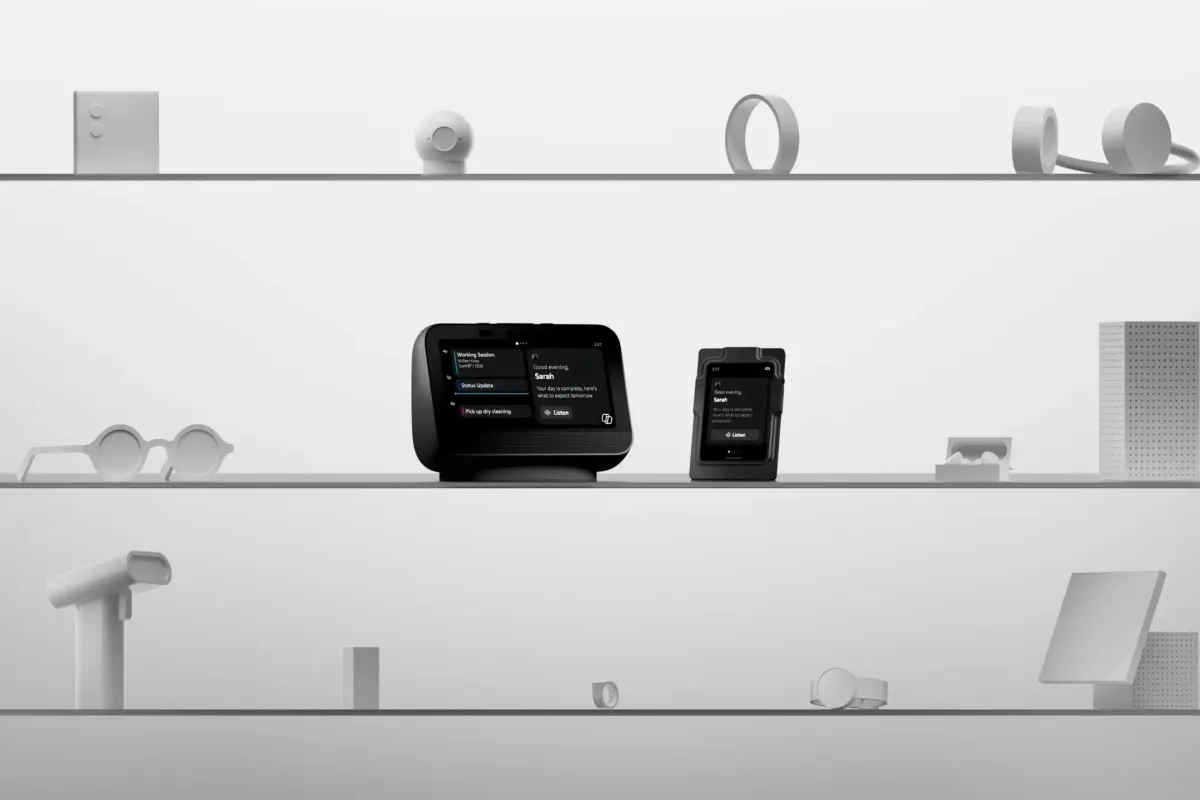
Microsoft unveiled Project Solara as a dedicated operating system designed to host artificial intelligence agents across purpose-built workplace devices, including smart security badges and touchscreen speakers. The platform emphasizes enterprise-grade authentication protocols and centralized IT administration while exploring how physical hardware can streamline computational interactions in professional environments. This initiative highlights the ongoing transition from cloud-dependent applications to localized processing capabilities that operate continuously within corporate facilities.
The next wave of workplace AI may not arrive as another app, but as an operating layer that coordinates agents, devices, and security controls. Microsoft Project Solara describes a possible operating system concept for AI agents on purpose-built workplace devices, helping teams move from screen-bound tasks to continuous, context-aware assistance while keeping enterprise security and administration in view.
Why workplace AI needs a shared operating layer
Organizations increasingly treat AI as shared infrastructure rather than a standalone productivity tool. When agents operate across devices, teams, and networks, they need a consistent runtime, predictable permissions, and centralized management. A shared operating layer can reduce fragmentation and make it easier to deploy assistants that fit into daily corporate workflows.
Understanding the Project Solara framework
Project Solara is described as a dedicated operating system concept for running AI agents across specialized workplace devices. Instead of relying exclusively on traditional computers, the platform standardizes how intelligent software operates on purpose-built hardware. That unified runtime can simplify deployment, administration, and integration of computational assistants into enterprise environments.
Core capabilities
- Standardized agent execution for corporate hardware and specialized endpoints.
- Centralized administration for remote device management and policy enforcement.
- Enterprise-grade authentication to secure access to agents, data, and workflows.
- Security and remote management architecture tailored to IT operations.
Security and remote management architecture
The architecture prioritizes controls that corporate IT departments can operate at scale. Administrators can monitor device health, enforce authentication standards, and manage agent permissions across distributed networks. This centralized approach helps address a persistent enterprise challenge: fragmented software solutions that create security vulnerabilities and complicate maintenance.
Purpose-built workplace hardware
Corporate wearables
Corporate wearables may include integrated sensors and connectivity modules. These devices can combine compact displays, cameras, directional microphones, and biometric scanners with standard networking hardware. Employees can summon specific computational assistants or review active task lists without accessing a central workstation.
A standard operational mode can display employee identification information, while an alternative configuration can prioritize agent management functions. The system can use modern identity verification standards to confirm user credentials before granting access to sensitive workflows.
Stationary companion devices
Stationary companion units may resemble conventional smart displays equipped with advanced processing capabilities. These units can feature integrated touchscreens that allow users to visualize agent status indicators and initiate voice-based conversations securely. The hardware can incorporate dedicated microphones optimized for conference room acoustics while maintaining strict data isolation protocols.
Enterprise deployment of such devices requires careful consideration of physical placement and network segmentation strategies. IT professionals must configure firewall rules that restrict outbound communication channels while permitting necessary telemetry updates from the cloud. Proper configuration helps ensure that ambient computing hardware does not inadvertently expose internal network resources to external threats.
Why expanding AI hardware matters
Traditional computing environments often require users to navigate multiple applications through graphical interfaces that demand sustained visual attention. Purpose-built devices aim to reduce cognitive load by placing computational resources directly within reach of physical workspaces. This transition reflects a broader industry movement toward ambient computing, where technology operates continuously in the background rather than requiring active user initiation.
Corporate environments face unique logistical challenges when deploying widespread software updates across many endpoints. Specialized hardware platforms can offer centralized control mechanisms that streamline maintenance procedures and reduce operational downtime. Organizations evaluating these solutions should weigh initial infrastructure costs against long-term efficiency gains in daily workflow management.
Security and administrative frameworks
Enterprise technology adoption requires rigorous verification protocols to prevent unauthorized access to proprietary information. The proposed platform can incorporate multiple authentication layers that verify user identity before executing sensitive commands or retrieving confidential data streams. IT administrators gain visibility into device health metrics and can remotely adjust permission levels across entire departments without physical intervention.
- Zero-trust network verification for all device communications.
- Real-time anomaly detection for continuous threat monitoring.
- Automated firmware update pipelines for consistent security patches.
Managing distributed computational resources introduces complex network topology considerations that traditional security models struggle to address. Modern infrastructure requires adaptive threat detection mechanisms capable of identifying anomalies in real-time communication patterns. Organizations exploring these deployments should align their practices with current engineering and security standards.
Challenges accompanying physical AI deployment
Hardware manufacturers must solve significant engineering hurdles regarding power consumption, thermal management, and miniaturization when embedding advanced processors into wearable accessories. Battery life remains a primary constraint for devices that require constant network connectivity and active sensor polling throughout extended work shifts. Engineers may explore energy harvesting techniques alongside optimized silicon architectures to extend operational duration without frequent recharging cycles.
Establishing clear boundaries between productivity optimization and employee surveillance remains a critical concern. Training programs that emphasize ethical usage guidelines are essential. Transparent data handling procedures help maintain organizational credibility.
Workplace cultural adaptation presents another substantial hurdle as employees adjust to environments where computational assistants operate continuously nearby. Human resources departments should collaborate with technology teams to draft clear policies that protect individual privacy while enabling legitimate business automation.
How enterprise networks support distributed intelligence
Corporate network infrastructure may require substantial bandwidth upgrades to handle continuous data synchronization between physical endpoints and cloud processing centers. Edge computing architectures can become essential components for reducing latency when agents process sensitive information locally before transmitting aggregated results. Network security teams should implement zero-trust verification models that validate every communication request regardless of its originating device or geographic location.
Supply chain logistics also demand careful planning to ensure consistent hardware availability across global office locations. Procurement strategies should account for potential component shortages and establish secondary vendor agreements to maintain deployment timelines. Financial analysts should calculate total cost of ownership metrics that factor in ongoing firmware updates, replacement cycles, and technical support requirements.
A practical evaluation approach
- Define the business use case, privacy boundaries, and data ownership.
- Pilot a small set of agents on controlled hardware with clear monitoring.
- Expand only after security, support, and user feedback are stable.
Conclusion
Project Solara represents a useful framework for ambient workplace computing by unifying AI agents across specialized hardware. Organizations that evaluate these platforms can gain clearer administration, stronger security controls, and a more coherent path toward AI-assisted workspaces. Leaders must balance innovation with privacy safeguards to ensure sustainable deployment across modern enterprise networks.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Christopher Holloway is the founder and director of Progressive Robot, a UK-based technology company. A full-stack engineer with more than two decades of experience, he works across PHP development, ecommerce, Linux infrastructure, technical SEO and AI automation, and writes here on technology, AI, hardware and software.

Comments (0)